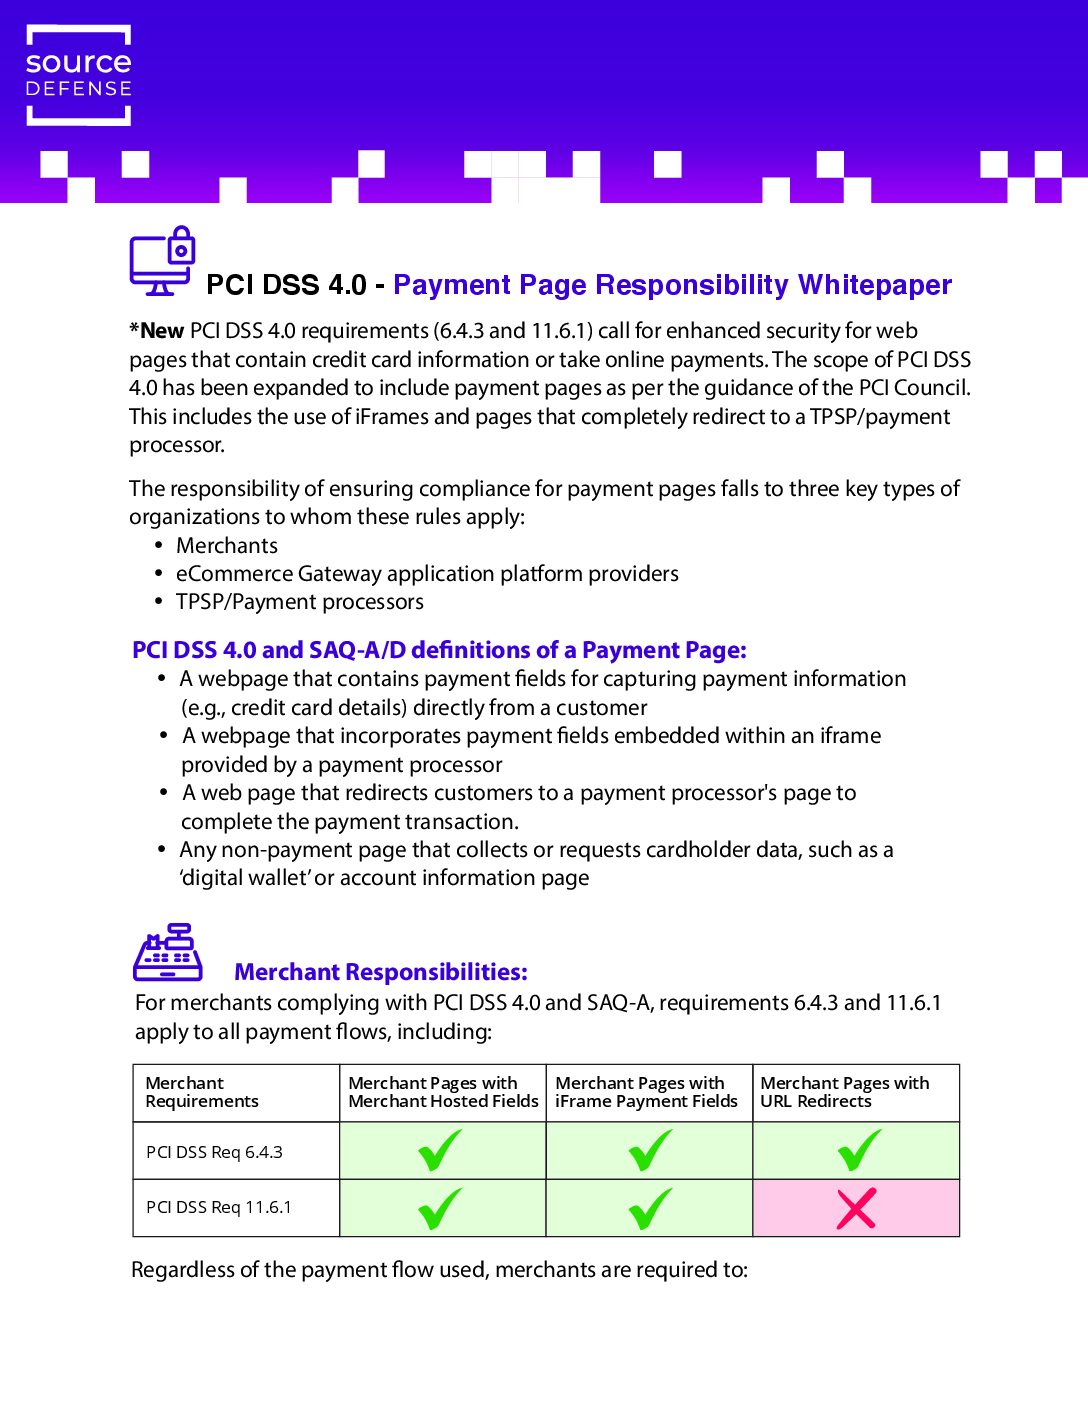
PCI DSS 4.0 – Payment Page Responsibilities
Learn what you need to do to meet new security standards for payment pages under PCI DSS 4.0
Get Your Free PCI DSS 4.0 Compliance Guide for Payment Page Security
The March 2025 deadline for PCI DSS 4.0 compliance is quickly approaching. Whether you’re a merchant, payment processor, or eCommerce platform provider, the expanded scope of PCI DSS 4.0 introduces new responsibilities for securing payment pages. Our in-depth guide, “PCI DSS 4.0 Payment Page Scenarios and Responsibilities,” provides clear, actionable steps to help you protect customer payment data and avoid potential penalties.
Discover the specific requirements for different payment methods and understand how to manage third-party code to prevent eSkimming, form-jacking, and other threats. Get the knowledge you need to stay compliant and keep your customers’ information safe.
What You’ll Learn in This Guide:
- Requirements for PCI DSS 4.0 Compliance – Understand the details of PCI DSS requirements 6.4.3 and 11.6.1 and what they mean for your payment page security.
- Managing Third-Party Risks – Discover how to authorize and monitor third-party scripts on payment pages to prevent unauthorized data access and potential breaches.
- Securing Different Payment Page Scenarios – Learn what you need to do to protect self-hosted fields, URL redirects, and iframe-hosted pages according to PCI DSS guidelines.