Register today and easily address these complex new requirements and more!
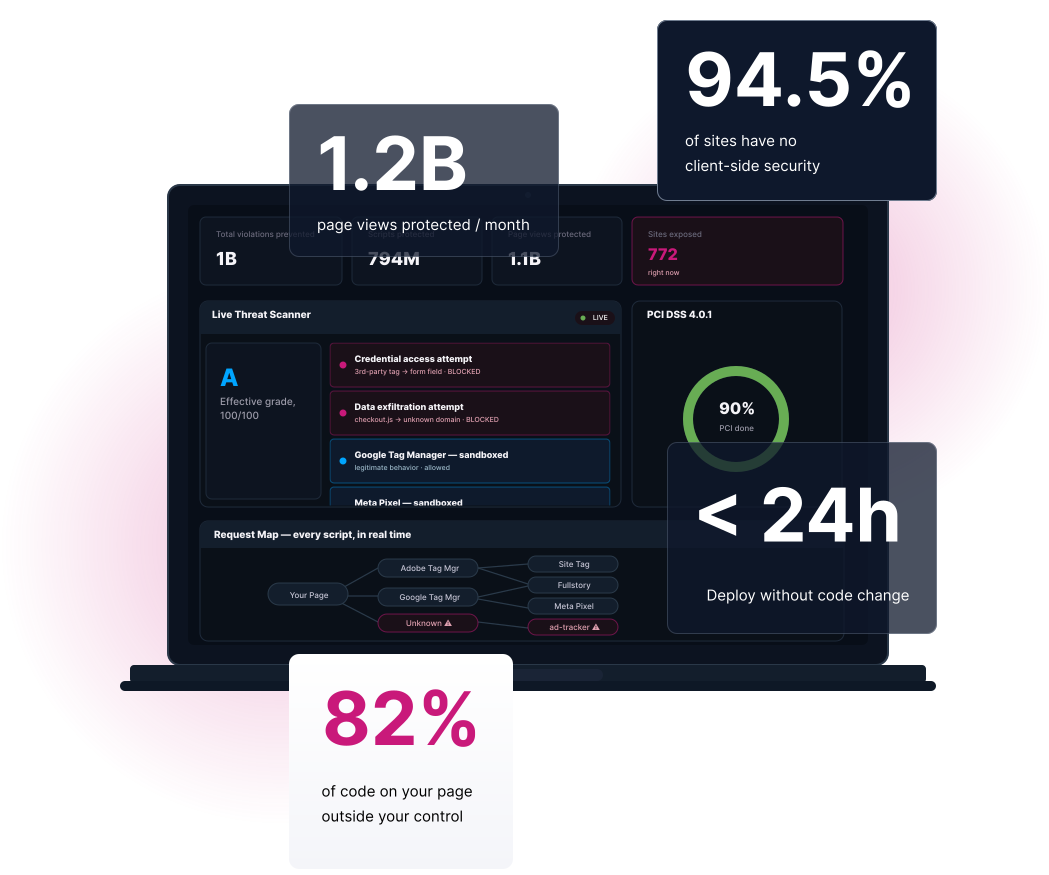
- Inventory: get an inventory of every script running on website payment pages, including a method for monitoring and tracking additions (required under 6.4.3)
- Justification: gain the ability to seek, document and manage justification of any scripts on website payment pages (required under 6.4.3)
- Integrity Monitoring: address the stringent requirements for integrity monitoring of HTTPS header and scripts found on website payment pages
- Offered weekly for the first 30 days
- Scaled back to monthly thereafter with the ability to upgrade for a fee
- Alerting: alert on suspicious and malicious activity found on website payment pages (required under 11.6.1)
- Blocking: feed alerts to your security team or automatically block all suspicious and malicious activity by upgrading (required under 11.6.1)
Frequently Asked Questions
How long does the solution take to integrate?
Integration is very simple. It requires the simple copy/paste of two lines of JS to your site’s head section.
How hard is the system to configure?
Our experts and machine learning can be leveraged to configure the system for you. Should custom configuration be required the administration console provides these tools.
Does the system require ongoing management and monitoring?
The system is designed to be low touch. The only time you will need to manage it, is when you integrate a new third party to your site.
Does this solution impact site performance, stability, and behavior?
The Source Defense solution is architected for deployment and administration simplicity. Although there is a small synchronous component to the solution, that adds approximately 100ms of latency. The solution then operates to isolate introduced 3rd party latency from your content ensuring that the impact of latency from loading multiple 3rd party JavaScript integrations are alleviated. Most deployment recognize a latency and stability improvement when deploying the Source Defense solution.
How do I know if my site is currently at risk to this attack vector?
Every website today that operates with 3rd party JavaScript is vulnerable to this attack vector. Today, it is difficult to find a website that doesn’t include multiple dozens of 3rd party JavaScript integrations. In fact, over 50% of all page requests are 3rdparty calls. In general, the more 3rd party scripts you use, the higher your risk exposure will be.
Does your system scale?
Yes, the system is built for scale, running of a strong CDN with several redundancies.