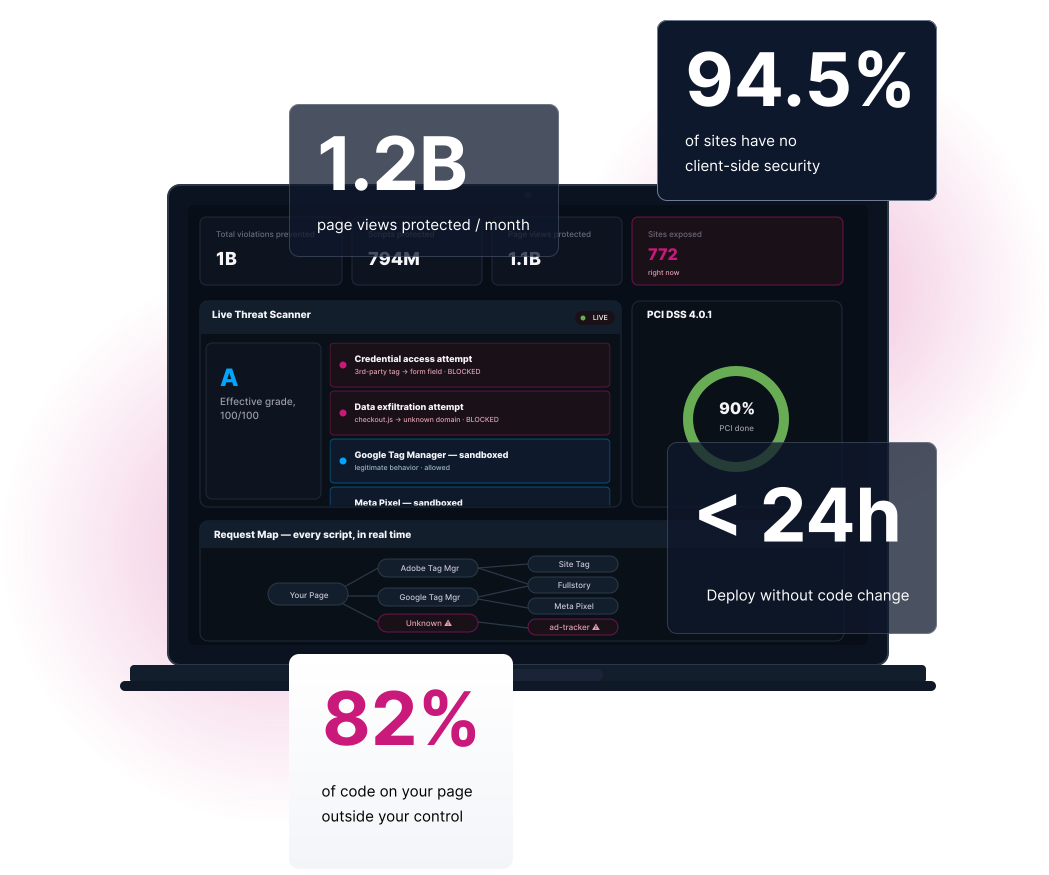
Simple process, minimal lift
- You sign up. We collect the basics and confirm which domains you want assessed.
- Within 48 hours we’ll start an external scan of your site requiring no code changes or lift on your end.
- You get results. Inventory, changes, risk signals, and recommended actions delivered in a usable format.
- You decide what’s next. Use it for internal risk reduction, to get moving on your PCI DSS compliance project or both.
Make client-side risk manageable
This is for the people who own 3rd party and website risk, even if it’s split across teams. Security and risk teams get visibility into what’s running on your site and the exposure your digital supply chain introduces. Compliance teams get the first steps moving towards PCI DSS compliance.
Frequently Asked Questions
Is this only for PCI compliance?
No. Compliance might be a driver behind eSkimming security, but the bigger issue is risk. This is designed to give you practical visibility and a path to reduce exposure across your site.
Will this break my site or slow down checkout?
No. This is an outside in view of your current environment – it requires no deployment and has no impact to performance.
What do I need to provide?
Give us the URLs you want to assess and a point of contact. We handle the rest.
What happens after I get the assessment?
Get a practical assessment of what’s running on your site and where your digital supply chain is introducing risk. Fill out the form above and we’ll follow up to confirm and get started.